The right approach is layered, not a single tool. Combine per-buyer stamping, expiring signed links and gated access as your first line of deterrence, then add monitoring so leaks surface quickly, and finally an enforcement ladder that runs from platform report to host DMCA notice, to search-engine delisting. Platforms such as BibliOWLteca and standards like Readium LCP give creators credible building blocks without needing to become a security expert.
TL;DR:
- Per-buyer stamping is a highly effective deterrent and traceability method for PDFs and templates, as it embeds buyer information into each file at delivery.
- Using expiring, signed download links with limited attempts and storing files outside the webroot significantly reduces passive link forwarding and guessing attacks.
- Streaming course content behind gated accounts offers better protection than downloadable videos, which can be easily shared once downloaded.
- Implementing core protections like moving files offline, enforcing HTTPS, and setting download caps can be completed in an afternoon, providing immediate leak prevention.
- Regular monitoring through search and alert tools, combined with documented takedown procedures, is essential to manage and escalate pirated content effectively.
Table of Contents
- What is digitaalse allalaadimise kaitse and why does layering work?
- How do you lock down downloads in one sitting?
- How do you actually get pirated copies taken down?
- How BibliOWLteca supports secure delivery for creators
- Get secure delivery running without the DIY setup
- Sources
- FAQ
What is digitaalse allalaadimise kaitse and why does layering work?
Digitaalse allalaadimise kaitse, or digital download protection, describes the combined technical and legal measures creators use to stop e-books, courses and templates being copied and redistributed without payment. In the industry, this usually gets discussed under three separate headings: deter, detect and enforce. Each layer has a distinct job, and skipping one weakens the whole stack.
Deter means making casual sharing harder and less appealing before it happens. This is where most of your effort should go, because it stops leaks at the cheapest possible point, before a file has even left your system.
Detect means finding leaks quickly once they occur, because a pirated PDF sitting unnoticed for six months does far more damage than one caught within a week.
Enforce means having a clear, repeatable process for getting copies removed once you find them, rather than improvising each time.
Per-buyer stamping (sometimes called watermarking) is the single highest-leverage deterrent for PDFs and templates, as seen in example setups like artist digital downloads shops that effectively protect their files. Rather than locking a file down, you embed the buyer's name, email or order number directly into the document at the moment of delivery. Practical guidance from SendOwl confirms this works because it is psychological as much as technical: buyers who see their own details on every page think twice before uploading it to a file-sharing site, and if a copy does surface, you know exactly which order leaked it.
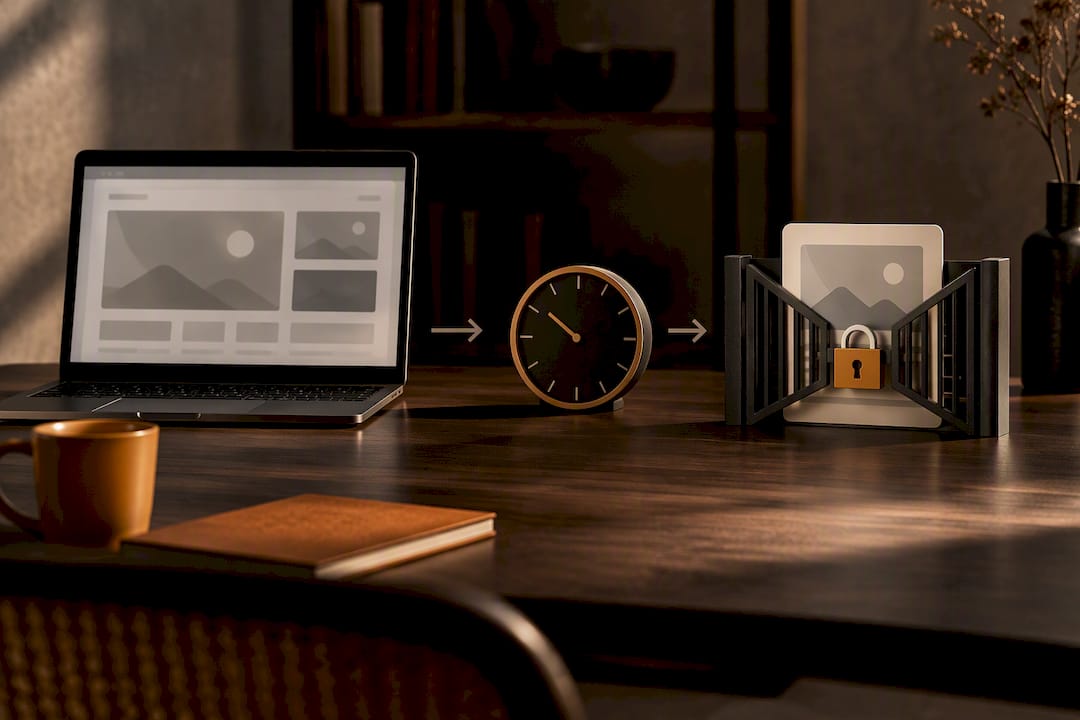
Signed, expiring download URLs and download caps close a different gap. A static link that never expires is an open invitation to forward, so Shopify's best-practice guidance recommends generating a temporary link per purchase, capping attempts at two or three, and storing files outside the public webroot so they cannot simply be guessed or crawled. Signed links combined with a tight download limit stop passive link-forwarding while barely inconveniencing a genuine buyer.
Courses need a different model. Gated account access, where video streams rather than downloads, protects far better than handing over an .mp4 file. Streaming keeps the content inside a login-controlled environment; downloadable video files, once out, are essentially uncontrollable.
- Gate video behind account login rather than offering raw downloads.
- Cap PDF and template downloads at two or three attempts per link.
- Store all delivered files outside the public webroot.
- Reserve full DRM for high-value catalogues where the cost is justified.
Formal DRM, and standards such as Readium LCP, sit at the far end of the spectrum. Readium LCP is a vendor-neutral system built specifically for EPUB and PDF publishing, and it is privacy-aware by design. But it requires certification for any server or client application that implements it, which brings real cost and technical overhead most independent creators don't need. EUIPO's guidance on DRM systems also flags that DRM authenticates copies and can track leak origins via metadata, but it must be designed with GDPR and privacy obligations in mind, not bolted on as an afterthought.
Pro Tip: Stamp files dynamically at the point of delivery rather than pre-stamping a master copy. Dynamic stamping means every buyer gets a uniquely traceable file without you having to manage dozens of pre-branded versions sitting on your drive.
How do you lock down downloads in one sitting?
You can put the core protections in place in an afternoon. Work through this checklist in order, and don't move to enforcement until the deterrents below are live.
- Move files outside the public webroot. If a file can be reached by guessing a URL, it will be found. Hosting it outside the directly accessible folder structure is the single cheapest fix available.
- Force HTTPS on every delivery link. Unencrypted links are trivially interceptable on public networks.
- Switch to signed, expiring URLs. Generate a fresh link per order rather than reusing one static address for every buyer.
- Set a download attempt cap. Two or three attempts covers genuine buyers who lose a file, without leaving the link open indefinitely.
- Turn on per-buyer stamping for every PDF, template or slide deck you sell.
- Add a one-page licence notice inside the product itself, stating what the buyer may and may not do with the file. This single page becomes your strongest piece of evidence if you ever need to file a takedown.
Once delivery is locked down, build a monitoring routine. DMCA Masters' practical framework recommends running quoted-title searches and distinctive-sentence searches from inside your own content, setting up free alert tools for your product name, sweeping resale marketplaces monthly, and running reverse-image searches on any course mockups or cover art. A small catalogue can manage this monthly; a larger one, selling weekly, needs it running at least fortnightly.
When you do find a leak, documentation makes or breaks the takedown that follows. Capture a screenshot of the infringing page, note the canonical URL, and timestamp the discovery, because a takedown notice without evidence is far less likely to succeed. If the leak traces back to a specific order through your stamping, revoke that buyer's access immediately and treat any refund request from that account with appropriate scrutiny before processing it.
How do you actually get pirated copies taken down?
Enforcement works best as a ladder, not a single email. Each rung is faster and cheaper than the one above it, so you only escalate when the previous step fails.
- Platform report first. Most marketplaces, forums and file-sharing sites have a built-in report or abuse function, and this is consistently the fastest, lowest-cost removal route according to DMCA Masters.
- DMCA or host takedown notice second. If the platform ignores your report or has no formal process, contact the web host directly. A valid notice needs the infringing URL, a description of your original work, a statement made in good faith that the use is unauthorised, and your contact details. Clear licence terms on your product page strengthen this considerably, because they prove the buyer agreed to specific limits.
- Search-engine delisting third. When a host is unresponsive or based somewhere enforcement is slow, requesting delisting from search results at least stops the leaked copy from being found by new searchers, even if the file itself stays live.
This escalation pattern, reported by ERR in coverage of Estonian anti-piracy policy discussions, reflects how enforcement actually plays out in practice across most jurisdictions and not just locally.
A monitoring or takedown service earns its cost once piracy becomes persistent across many hosts rather than a one-off leak. But be clear on what a takedown buys you: cleanup, not prevention. It removes a copy after the fact; it does nothing to stop the next one, which is why the deterrent layer still matters more than the enforcement layer over the long run.
How BibliOWLteca supports secure delivery for creators
Selling through a platform that handles delivery mechanics well removes a chunk of this workload before you touch a checklist. BibliOWLteca provides secure delivery controls and multi-currency payment processing built specifically for creators shipping e-books, courses and templates. Many sellers use combinations such as per-buyer stamping on documents, expiring links on file downloads, and gated access for course content rather than raw video files. For deeper background on the legal side, BibliOWLteca's own guide to copyright for digital content and its GDPR checklist for course sellers are worth reading before you scale. Once piracy becomes persistent and spreads across multiple hosts, that's the point to bring in dedicated monitoring or legal support alongside platform controls, not instead of them.
— BibliOWLteca
Get secure delivery running without the DIY setup
Building signed links, stamping and gated access from scratch takes real developer time most creators don't have to spare. BibliOWLteca is built for exactly this: secure digital delivery and delivery controls are native to the platform, so you're not stitching together plugins to protect a PDF or a video course.
There are no monthly fees on the Creator Plan, only a transaction fee starting from €0.99 per sale, so the cost only shows up once money is actually coming in. If you sell e-books, courses or templates, browse the product categories to see how listings and delivery are structured before you commit. For creators dealing with high-volume, persistent piracy across many channels, pairing platform-level protection with a dedicated monitoring or takedown service still makes sense, but for most sellers, getting delivery right on a platform like this is the first and most important move. Set up your store and check how stamped, expiring downloads work in practice.
This article is general information, not a substitute for advice from a qualified lawyer. Consult a qualified legal professional about your own circumstances before acting on anything here.
Sources
- EUIPO — Anti-counterfeiting and anti-piracy technology guide: digital rights management (DRM) systems
- DMCA Masters — How to protect digital products from piracy
- Shopify — How securing downloadable content works: best practices (2026)
- ERR — Fighting digital piracy permanently on the agenda (Kalle Laanet)
FAQ
What is the fastest way to stop a leaked e-book from spreading?
Report the infringing listing directly to the platform or marketplace hosting it, since this route removes content faster than any other channel according to DMCA Masters. If the platform doesn't respond, escalate to a DMCA notice sent to the host directly.
Does DRM actually stop piracy completely?
No protection method, including DRM, stops piracy completely. DRM can authenticate legitimate copies and trace leak origins through embedded metadata, per EUIPO's guidance, but lighter deterrents like per-buyer stamping and expiring links stop far more casual sharing at a fraction of the friction.
Is per-buyer stamping worth it for a small catalogue?
Yes, stamping is worth setting up even with only a handful of products, because it takes little to implement and works as both a psychological deterrent and a traceability tool if a file does leak. It is one of the highest-leverage steps in the deterrent layer.
How much does BibliOWLteca cost for creators selling downloads?
BibliOWLteca's Creator Plan carries no published monthly fee; you pay a transaction fee starting from €0.99 per sale, detailed on the pricing page. This means costs only apply once a sale has actually gone through.
Should courses be sold as downloadable files or streamed?
Streaming behind a gated account is generally safer than offering downloadable video files, because once a video file is downloaded it is effectively uncontrollable. Gated streaming keeps content inside a login-controlled environment throughout, which is the model most course platforms are built around.